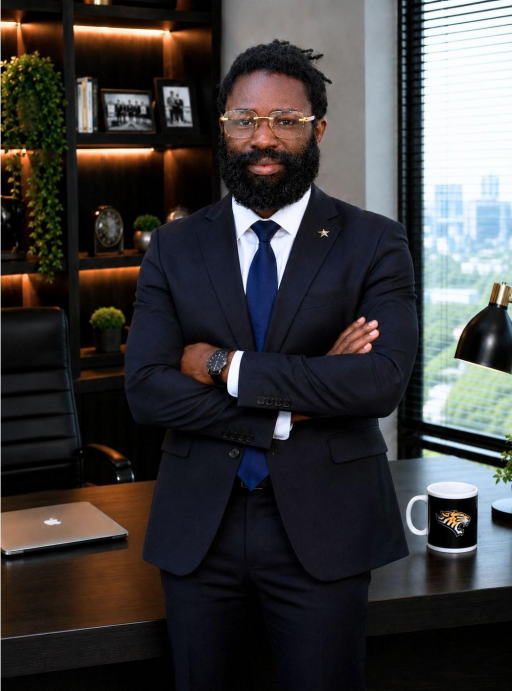
In an interview, the Towson-based cybersecurity practitioner, Ph.D candidate, researcher, and community educator reflects on Lagos, AI security, national resilience, service, and the patience required to learn golf and fishing from the ground up.
Towson, Maryland | June 2026
Michael Funskin speaks about cybersecurity with the calm of someone who has spent years troubleshooting real systems, not just talking about abstract threats. His career has moved from hands on technical support in Lagos to security operations, cloud defense, AI-focused research, and workforce development in Maryland. He is CISSP and SSCP certified and is pursuing a PhD in Information Technology at Towson University, where his work increasingly sits at the intersection of cybersecurity, AI governance, operational resilience, and human-centered security education. He also leads Certification Readiness and Workforce initiatives through the ISC² Annapolis Junction Chapter, building learning spaces for students, career changers, veterans, and working professionals.
“Cybersecurity is not only a technical field. It is also about people, judgment, communication, and preparation before the crisis happens.”
Q: You started your career in Lagos before coming to the United States. When you look back, what did that early period teach you?
Funskin: Lagos taught me how to solve problems with whatever resources were available. At the time, the internet became my primary source and medium of learning, alongside knowledge I gained from friends. I started by using Google and watching online videos to learn how to repair mobile phones. What began as curiosity gradually became a business.
I opened a service and repair center where I initially worked on BlackBerry phones and later expanded into repairing Apple devices, including iPhones, MacBooks, and iPads. As the business grew, I also began selling phones, MacBooks, and other devices. That experience marked the beginning of my interest in IT operations and technical support.
Working directly with customers taught me how to deal with real users, real systems, and real pressure. When a device fails, a network goes down, or someone cannot access a system, theory alone is not enough. You have to listen carefully, ask the right questions, isolate the problem, and fix it without creating another issue.
My physics background also helped because it trained me to think in terms of systems, patterns, and causes. Those early experiences in Lagos became the foundation for my later work in IT and cybersecurity.
Q: What moved you from IT support into cybersecurity?
Funskin: The move happened naturally. In support, you begin to see patterns. You notice weak passwords, poor access control, unpatched systems, missing backups, and users who are doing their best but have not been trained to recognize risk. Over time, I became less interested in only fixing incidents after they happened and more interested in preventing them. At Mars Media, that became a much bigger part of my work. I worked with SIEMs and SOC tools, vulnerability scanning, access control, endpoint protection, network segmentation, and security assessments. That period helped me understand that cyber defense is not one tool or one checklist. It is a continuous process of monitoring, improving, documenting, and helping people make better decisions.
Q: Your current work at Dream Chase Technology sits between IT operations and security. How do you describe that role?
Funskin: I describe it as practical defense. The work includes securing infrastructure, supporting endpoint protection, vulnerability scanning, patch tracking, VPN configuration, and cloud security practice environments. I work with tools such as Microsoft Defender, CrowdStrike Falcon, Nessus, Qualys, AWS Security Hub, and GuardDuty. What I like about the role is that it keeps security close to operations. Security has to work in the environment people actually use. A policy that cannot be implemented well is not enough. A tool that produces alerts no one can act on is not enough. My goal is to help reduce risk in a way that is realistic.
Q: You are also pursuing a PhD at Towson University and supporting CLARK as a doctoral research assistant. What is driving your academic work right now?
Funskin: The big question for me is how we prepare people and organizations for emerging cyber risks, especially as AI becomes part of security operations. At Towson, I support CLARK by helping align curricula with the DoD Cyber Workforce Framework. That work matters because the cyber workforce cannot be built only through theory. People need structured learning paths, practical skills, and a clear understanding of what different cyber roles actually require. My research interests include AI safety, AI security, governance, autonomous threat response, AI risk, ethical AI, and cyber resilience. I am interested in how we use AI responsibly without losing human judgment.
Q: Your recent research spans vulnerability discovery, social media analysis, backdoor attacks, and health prediction. How do those projects connect?
Funskin: My research focuses on cybersecurity, artificial intelligence, machine learning, and the security and reliability of intelligent systems. Although I have worked on different problems, a common theme is understanding how technology can improve decision-making while addressing the risks that come with it. One of my publications is CyberRec: An AI-Powered Hybrid Text & Knowledge Graph Recommender for Software Vulnerability Discovery, published in the proceedings of the 2026 IEEE/ACIS International Conference on Software Engineering Research, Management and Applications (SERA). The study explores how text analysis and knowledge graphs can work together to improve software vulnerability discovery and recommendations.
Another research project, Evaluating Backdoor Vulnerability and Defense Baselines in Traffic Sign Recognition Networks, examines the security of machine learning models used in traffic sign recognition. I investigated how an attacker could compromise a model during training by introducing a hidden trigger that causes incorrect predictions. In one experiment, poisoning just 5% of the training data produced a model that maintained 96.56% accuracy on normal traffic signs while achieving an 88.67% attack success rate when the trigger was present. I also evaluated a pruning and repair defense, which reduced the attack success rate to 80.86% but did not completely eliminate the vulnerability. This highlights why high prediction accuracy alone is not enough to establish that an AI system is secure.
I also co-authored Learning Parents’ Reactions to Children’s Use of Social Media, a study examining how parents perceive their children’s use of social media platforms. We analyzed 3,991 Reddit comments using a transformer-enhanced sentiment analysis model combining TF-IDF, self-supervised pseudo labeling, and DistilBERT. The model achieved 96.64% classification accuracy. One interesting finding was that parental opinions were not simply positive or negative. Many parents expressed mixed or conditional views, recognizing the benefits of social media while remaining concerned about children’s online safety, privacy, and exposure to harmful content.
Another area of my research involves machine learning for heart disease prediction, exploring how predictive models can support data-driven decision-making in healthcare.
What connects these projects is my interest in building intelligent systems that are effective, secure, trustworthy, and useful in real-world applications. As AI becomes increasingly integrated into critical systems, I believe we need to pay much closer attention to how these models are developed, evaluated, secured, and deployed.
Q: You have also been speaking more about AI safety. Why is that an urgent issue?
Funskin: AI safety should not be treated as a side project or a public relations phrase as these frontier AI labs are doing. The scale of investment going into building larger and more capable AI systems is enormous, but the work dedicated to safety, assurance, testing, governance, and long-term reliability is still too small by comparison. That imbalance is not only about funding; it is also about people. We need more AI safety engineers, security engineers, technicians, auditors, policy professionals, risk analysts, red-teamers, incident responders, and educators who understand how these systems can fail in real environments. When AI is used in healthcare, finance, education, defense, critical infrastructure, or security operations, safety cannot be added at the end. It has to be designed into the system, tested before deployment, monitored after deployment, and governed by people who understand both the technology and the public consequences. Cybersecurity has already taught us what happens when innovation moves faster than protection. With AI, we should not repeat that mistake at national scale.
Q: You often use the phrase national resilience. What does that mean to you?
Funskin: National resilience means the ability of a country, its institutions, and its people to keep functioning under pressure. Cybersecurity is part of that because almost every critical service now depends on digital systems. Hospitals, banks, schools, transportation, government services, food supply chains, and small businesses all rely on technology. AI adds another layer because it can strengthen defense, but it can also increase the speed and sophistication of attacks. To me, championing cybersecurity and AI as part of national resilience means building systems that are secure, adaptable, transparent, and human-centered. It also means investing in people, not just products.
Q: Your role with the ISC² Annapolis Junction Chapter is focused on certification readiness and workforce development. Why is that important to you?
Funskin: Technology is constantly changing, and cybersecurity professionals cannot afford to rely only on what they learned several years ago. New tools, attack techniques, regulations, and technologies continue to emerge, so the workforce must continually build new skills and update its knowledge to keep pace with the field. That is one reason certification readiness and continuing education are so important to me.
I also know what it feels like to grow into cybersecurity step by step, so I care about making that pathway clearer for others. Through the chapter, I help organize certification study groups, workshops, mentorship programs, and continuing professional education opportunities. I am especially interested in helping high school graduates, college students, transitioning veterans, career changers, and working professionals find realistic ways to enter the field or advance within it.
Certifications such as CISSP, SSCP, and Certified in Cybersecurity are not magic tickets, but they can provide structure, shared vocabulary, confidence, and evidence of continued professional development. More importantly, workforce development is not simply about filling open positions. It is about building capable, adaptable, and responsible defenders who can continue learning as the threat landscape evolves.
Q: You have talked about cybersecurity as a human challenge. What do people misunderstand about the field?
Funskin: A lot of people think cybersecurity is only about hackers, tools, and code. Those things matter, but the field is much broader. Risk management, communication, training, documentation, governance, compliance, incident response, and leadership all matter. Sometimes the strongest control is not a complicated technology. It may be a well-trained team, a clear process, a properly tested backup, or an executive who understands why an investment matters before a breach happens. Security fails when people treat it as a one-time purchase. It works better when it becomes part of how an organization thinks and operates.
Q: Outside your professional work, golf seems to have become one of your learning projects. How is that going?
Funskin: Honestly, I am not good at golf at all. I enjoy it, but I still have a long way to go. Some days I feel like I am creating more divots than distance. What I like about golf is that it humbles you immediately.
You can understand what you are supposed to do, and the ball will still go somewhere completely different. That is frustrating, but it is also why I keep going back. The ISPE Chesapeake Bay Area golf clinic events at P.B. Dye Golf Club have helped because they give beginners like me a structured place to learn and practice. You get coaching, you watch other players, you ask questions, and you realize that improvement is built one swing at a time. Attending golf tournaments has also helped me appreciate the discipline of the sport. Good players make it look effortless, but when you try it yourself, you understand how much repetition and focus are behind every shot.
Q: You also fish, hike, and spend time outdoors. Is that another area where you are still learning?
Funskin: Definitely. I am a novice at fishing. I am still learning the basics: knots, casting, patience, reading the water, and knowing when to stop fighting the process. Fishing is very different, you cannot force anything. You pay attention, adjust, and wait. Hiking and being outdoors help me reset. When you spend a lot of time with screens, logs, alerts, documents, and research, being outside reminds you to slow down and notice things beyond the immediate problem in front of you.
Q: Volunteering at First Fruits Farm is also part of your life outside work. What draws you there?
Funskin: First Fruits Farm is meaningful because their mission is to grow food and help feed people who are hungry. Volunteering there is physical, direct, and humbling. You are planting, harvesting, sorting, or helping move produce that will go to people who need it. It is just about showing up, doing the work, and supporting a mission that feeds the poor and hungry.
Q: You are also active in the Towson University Alumni Association. How does that fit into your broader community work?
Funskin: Towson has been very important in my journey, so staying connected matters. Being active in the alumni community is a way to stay connected with students, graduates, faculty, and professionals who are building their own paths. Universities are not just places where people earn degrees. They are networks of support, opportunity, and identity. For me, the Towson alumni community is part of that. It helps me stay connected to the institution that shaped my U.S. academic experience and gives me opportunities to support others coming behind me.
Q: You also enjoy classical music and attend the Baltimore Symphony Orchestra. What does music give you that technology does not?
Funskin: Music gives me a different kind of focus and release. Classical music makes me slow down. When I attend the Baltimore Symphony Orchestra, I am just listening. The BSO is widely recognized as one of the best orchestras in the world, and hearing that level of discipline and coordination in person is powerful. A symphony is a good reminder that excellence is collective. Every person has a role, timing matters, and the final result depends on many people listening to each other. That connects to leadership and security more than people might think. At the same time, I am also a House Music DJ, and house music is my type of vibe. It has rhythm, movement, repetition, soul, and community. Classical music gives me structure and depth; house music gives me energy and expression.
Q: When people read your story, what do you hope they take away?
Funskin: I hope they see that growth is not always a straight line. My path started with physics and technical support in Lagos. It moved through security operations, cloud work, AI research and community service. Each stage taught me something different. I want people to understand that cybersecurity needs people with different backgrounds and different strengths. It needs technical skills, but it also needs patience, ethics, communication, humility, and service. If my story encourages someone to start, continue, or come back after a setback, then that matters to me.
By the end of the conversation, Funskin’s story feels less like a simple career profile and more like an argument for resilience itself. He has moved across countries, roles, technologies, and communities, but the through line is consistent; learn carefully, serve where you can, communicate clearly, and prepare before the pressure arrives. Whether he is helping professionals study for certification, researching AI driven vulnerability discovery, working through security operations, volunteering on a farm, or trying to keep a golf ball on the fairway, Funskin returns to the same lesson. Progress is built through disciplined practice, community, and the willingness to keep learning.
Michael Funskin is a cybersecurity practitioner, researcher, and educator specializing in AI security, governance, and operational risk. He is pursuing a PhD in Information Technology at Towson University. His work focuses on translating emerging AI and cybersecurity risks into practical, measurable, and accountable security frameworks, with particular interest in the safe and responsible deployment of AI within operational environments.
Daily magazine for entrepreneurs and business owners